Windows applications are at the core of what we do in many sectors from running business systems which process payments and manage our records to connecting with remote servers and operating industrial scale equipment. While these applications may be the backbone of our business they also handle very sensitive data and in many cases have direct access to the operating system which in turn puts forward a great deal of pressure regarding security in their design and implementation. A program may function as intended but still leave the user open to data theft, unauthorized use, or a system which has been taken over by a hacker.
That which brings about these issues is often a result of everyday programming choices — for example to not properly validate user input, to save passwords in an insecure manner, to request more permissions than is necessary, or to use out of date software libraries. By studying Windows application security issues we are able to identify these risks early on in the development process. By way of applying secure code practices, choosing the right auth methods, limiting what the app is able to do, and to test the software often we as developers are able to put together applications which are much more secure and reliable for the end users which in turn increases the value of the application.
Windows Application Security
Windows application security is about protecting desktop programs, background services, utilities and other Windows based software against unauthorized access, info disclosure, malicious code injection and system disruption. As opposed to functional testing which is done to see if the application does what it is supposed to do, security testing looks at how the program does or does not — handle unexpected inputs, unauthorized actions, broken dependencies, and hostile environments. A Windows application may interface with the file system, Windows Registry, local databases, network services and other OS components. Each of these interactions present security issues if proper permission settings, input handling, and data protection are not put in place. For example an app which handles customer info must stop that info from being accessed by unauthorized users, also a utility which changes system settings must see that it does not perform privileged actions based on untrusted input. Thus developers must have a grasp of their application’s inner workings as well as the security features which Windows provides.
Security issues can present at any point in the software development lifecycle. At design time, we see developers that ignore auth requirements or that play it safe in assuming users will do what they are supposed to. In implementation, we find out that they have run database queries which are not secure, they are mishandling of sensitive info, also at this stage they may allow untrusted data to determine file paths. In maintenance we note that use of out of date dependencies and unpatched components is a large issue. These issues put forth that security has to go beyond the final feature that is thrown in right before release. Rather what we see is that security should be a part of the application architecture, the coding standards, the testing practices, the deployment config and the maintenance plans. Microsoft reports security features and also gives out development guidance which is a great resource for programmers to create better Windows software, but that is only useful if used properly. A secure app is one that takes in the right platform features, makes smart programming choices and is also always looking out for new threats which are out there.
1. Input validation issue.
Improper input validation is a primary cause of what we see in terms of application break ins. It is when software does not properly check out that which it should be processing in relation to what the application requires. In Windows applications we see input from text fields, config files, imported docs, network requests, command line args, and external processes. Devs may assume that users will put in what is expected, but attackers will put in what is not expected large scale, out of place, broken data to get unexpected results.
Per application structure, what we see is that which goes unvalidated can play a role in SQL injection, path traversal, command injection, denial of service issues or other security issues. For instance a customer info app may take in a search term and run it as is into a database query. If the app is putting together SQL statements out of raw input and query text, an attacker may change what that query does. The issue is not that input has odd characters in it, it is that the program gives that which is untrusted too great of a role in what it does.
Unsafe Input Handling and Safer Alternatives
In a Windows application developed in C# which queries a customer database we see that an unsafe implementation may put together a query by use of a user’s search input in the SQL statement. That which is seen is a large opportunity for SQL injection in which the database in turn may parse out some of that put together value as a command rather than just data. Instead a better way is to go with parameterized queries which in turn keep the SQL command separate from the user input values. Also developers should validate input according to what it is supposed to do, for example check that a number is in a certain range or that an ID is in the right format. Such validation should take place at the server or at a trusted processing stage as security decisions based on data may be defeated at the client side. Also included in this is setting input size limits, to handle parse errors gracefully, and to not assume that data from local files or internal services is clean and safe.
An invalid input should trigger a pre-defined response which in turn will not cause a crash and which also does not expose internal server info. Using a mix of validation with respect to the given context, proper encoding, safe API practices, and detailed error handling we can avoid the use of unexpected data as an attack vector.
2. Poorly Secured Credentials.
Windows applications at times require authentication of users, access to remote services, or connection to databases. We see that they may use passwords, API keys, access tokens and other types of credentials. It is out of question that such info should not be stored in plain text, embedded in source code, or put in public config files which may be accessed by unauthorized persons. For instance a dev may put in a database password right into a C# source file for easy deployment.
As soon as the app is out there and in use, someone that gets the source code or has access to the compiled program may get that credential. Also private repos and dev machines which may be breached also play a role. A single credential leak may go past the intended application because we see that developers also use the same passwords around and may give service accounts wide access to databases, cloud platforms and other systems.
Protecting Credentials in Windows Applications
Developers must steer clear of hard coding secrets and should choose a credential storage which is right for the application and its deployment environment. Windows has security features like the Windows Credential Manager and Data Protection APIs which do protection of sensitive info at rest. What feature to use depends on if the app is running under a user’s account, as a service, or is to get credentials from a managed secret store. Also do not write out sensitive data to typical log files, put them in error messages or diagnostic reports without proper protection. For password handling go through established auth systems for apps which store password for their own auth purposes use proven password hashing algorithms with unique salts instead of reversible encryption or plain text storage. Access tokens should have low permissions and short lives when practical and exposed credentials should be revocable.
A secure design is also one that reduces the number of elements which have access to a secret. For a remote service connection issue, we see that developers should think if there is a way to outsource the authentication process to a trusted third party identity provider or if we have at our disposal a managed identity solution in the environment we are deploying to. Also for desktop apps which we are to put in the users’ hands we should not include a so-called secret which gives all instances of the application free rein to a shared backend. Also any secret that is put into a client app must be taken to be available for the taking. Rather we should for the most part have the trusted server do the authorizing of sensitive actions which in turn will allow it to put in place access controls and keep privileged info out of the users’ reach. We do this which in turn lessens the damage done in case of application compromise and also makes it a simpler task to change our credentials after a security incident.
3. Over privilege and abuse of access rights.
Excessive permissions present large attack surfaces which in turn protect info that should be private. A Windows app that asks for admin rights for non critical processes increases what is at risk in case of a break in. If we have a flaw in a very privileged program an attacker may take over assets which normally would not be at his disposal.
Also when apps run background services with full access, create modifiable files, or give out wide open permissions there are similar issues. Devs at times ask for higher privileges for ease of install or to avoid permission issues during dev but convenience is not a reason to grant an app more power than it needs to do what it is designed to do.
Applying the Principle of Least Privilege
The principle of least privilege is to give each user, process, and application component only what it needs to do its job. We recommend that developers study least-privilege access and apply this principle in the design of Windows apps. For example a desktop app which edits documents in a user’s personal folder usually doesn’t require admin access. If at large scale a specific action does require elevation then the application should ask for it only when that is the case and to keep the privileged action separate from everyday user interface functions. Windows User Account Control is a tool to help users in their decision making for elevation requests but it is not a substitute for good application design and authorization. Also applications should see to it that not all users have write access to executary dirs, service config files, or any other which via modification may lead to code execution.
Least privileged access is a must for all of an application’s components. Windows services must run under proper restricted accounts, database connections should have very narrow permissions, and we check in at the point that sensitive resources are used. We also note that it is a false security to present a button or a menu which a user does not have authorization to use — users may find a way to trigger that functionality from other means. What is important is to secure the action itself. In the course of programming and testing, developers must study the level of permission that each part of the system needs, and get rid of extra access. We see that this practice reduces the security impact when a part of our system is breached, or when there is accidental misuse or config error, all while still enabling the useful features of the application.
4. Risky File Operations.
File out management presents a number of security issues which in turn see Windows apps which create, open, modify, import, and delete files very often. We see problems play out when a program which takes in file paths from users, which it then follows to unexpected directories, which in turn overwrites protected files or which assume that a file name means the file is safe. Also very common is path traversal in which putting together input results in an app which accesses files beyond what was intended.
For example a doc management app which takes a file name and which puts it right into a directory path. If the app does not check the end result of that path, a malicious file name may steer the program to a different location. Also we see issues of temporary files which are unsafe, predictable file names, directory settings which are too permissive and race conditions in which a file changes between the time it is checked and the time it is used.
Implementing Safer File Access
Developers should check that file names and paths meet what the application requires, resolve paths to their canonical form, and also make sure the results are within the allowed directory. But a simple string-prefix comparison does not work in all path validation cases as path separators, symbolic links and other file system issues may play a role. We recommend that applications use the Windows and.NET file system APIs which are put forward for this purpose, to apply proper access controls and also to take into account how reparse points and links play into the security picture. Where it is practical to do so, programs should work with secure file handles instead of again and again checking a path and then opening it. For temp files we should use APIs which do not produce predictable names or have unsafe creation patterns and also see to it that sensitive files have restricted permissions. Also do not have files executed automatically which are imported and do not assume that a familiar file extension means it is safe.
File operations should put in place measures to deal with failures, concurrent access, and out of the expected content. For example a program which imports customer records should check the file’s structure as expected and handle which do not meet that structure without which do in turn corrupt present data. Before carrying out operations that are destructive, applications should confirm that the target is in fact what they think it is and also that the current user has permission to modify it. When updates include a series of related files, developers should put in transactional approaches or safe replacement practices into play which in turn reduce the chance of partial writes and data corruption. File access should be to the directories the application truly needs, also executable and which control privileged behavior should not be stored in which untrusted users can modify. With careful path handling, access-control enforcement and robust error handling file related vulnerabilities are made much less likely.
5. Weak Dependencies and out of date Libraries.
Modern in most cases we see that which is developed by a single team is a thing of the past for Windows apps. They usually depend on external packages, frameworks, run time components, drivers, and third party libraries. That which is dependent on these elements reduces the development time and also provides very useful features but at the same time introduces security issues when these external elements have known vulnerabilities or are no longer maintained. Also an application may present security issues even if its own source code is secure. What an attacker may do is to use a weak point in one of the included components.
For example an out dated image processing library may have an issue which is triggered by specific files that cause unsafe action. Also a vulnerable networking package may put an application at risk of attacks which use malformed responses or unexpected requests. Also what we see is that dependencies may bring in supply chain risks if we get into the build process something which is malicious or has been compromised.
Managing Dependencies Securely
Developers must maintain a record of direct and indirect dependencies and use trusted package sources. For.NET apps which is a case in point, package management tools will point out what the issues are with the present set of dependencies as well as their versions, also at the same time security scanners which are supported will put to notice some known vulnerabilities. Teams are to be tuned into related security advisories, to repair what is broken immediately and to test changes before putting them out there. At times pinning down dependency versions or the use of a lock file is a good practice which in turn makes the build more of a predictable affair, that said this should not be used as a reason to keep what is out dated. Automated updates are a great help in reducing maintenance effort but what is put forth by the automated process has to be reviewed and tested first. Also do away with unused packages which you are not using, what you do not need increases the attack surface of your application and also adds to the maintenance load.
A secure dependency management process should go past looking at just the latest version number. Developers should look into if a package is indeed being actively developed, if the publisher is one to trust, if they have a put in place security report process, and if the application truly requires that which is being presented. Build environments should put in access controls for who can modify dependencies and should also avoid to the great extent that they can, to download packages from untrusted sources. Where it is at all possible use software composition analysis and software bills of material to see what is in a given release. If a team is unable to update a vulnerable dependency right away they should do a specific assessment of the exposure, apply any available mitigations, put in place what restrictions of function they must for the issue at hand, and document out the risk which remains. Dependency management is an ongoing security issue at large rather than a one time dependency installation task.
6. Weak Authentication and Authorization Protocols.
Authentication reports the what and who of access to a system which authorizes what actions that entity may perform. To mix these up is to open the door to large scale issues. For instance a user may pass authentication but via altering a request parameter see into another’s data which they should not have access to. Also we see applications which have home rolled password systems which do not protect against brute force login which in turn leaves accounts open to being guessed at.
Also which rely on local flags to determine admin level which can be played with if not secured by a strong auth scheme. In secure Windows development for instance it is a must that we have good identity proofing and that we apply permissions the same way across all critical functions.
Choosing Appropriate Authentication Methods
In whichever way possible Windows apps should use present identity systems instead of coming up with their own auth protocols. Based on the setting at hand which may include Active Directory for identity management, Microsoft Entra ID, or some other trusted identity provider appropriate options may be used. We recommend developers use secure auth libraries, protect auth tokens, and validate identity provider responses as per the chosen protocol. Multi factor auth can add an extra layer of protection for sensitive accounts and operations. For apps which have their own accounts we recommend a secure auth design which includes protection against repetitive failed attempts and has appropriate recovery procedures. Apps should never store passwords in plain text and also it is not enough to encrypt passwords with a reversible key. We recommend secure password verification.
Authorization must be a separate process from authentication. After a user is identified the application must validate if the said user indeed has permission for the requested resource or the particular action they wish to carry out. In the case of a payroll application for instance do not base the ability to change salary info from a successful login of the user, rather use the user’s role and specific permissions as the go to. Also, an application should put into play trusted application components for authorization especially when the remote user is accessing shared data on the server. We also suggest that developers look at session end times, revocation of tokens, disabling of accounts, and changes in user permissions. In terms of testing, we should see through attempts to get in without permission, tampering with the ID, reusing old tokens, which may have been invalidated and invoking methods for which the average user does not have access.
7. Security Assessment and Secure Development Practices.
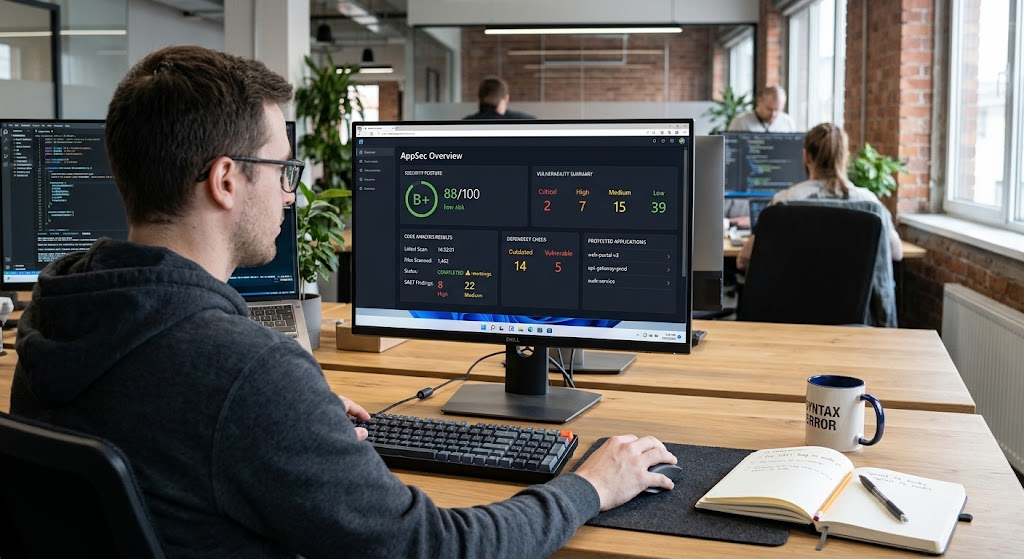
Secure coding is a way to reduce the number and severity of vulnerabilities in applications but it cannot ever completely eliminate the risk that a security defect will be present. In the Windows development environment we see that a combined use of static code review, automation of security analysis, focused security tests, and analysis of how the application is expected to work in the real world is what is done. Static application security assessment tools will find out some risky issues without actually running the software but dynamic assessment looks into the issues as the application is run.
Also, dependency scanning will point out which included packages are known to be at risk and fuzz testing is for when unpredictable data is used with the app. This is in addition to routine functional testing, that often does not include attacks from bad actors or from going outside the normal functions of the app. At the same also developers have to look at the application manifest, service config files, permissions, the way the app handles log in, logging outputs, and the set up for application release that is where we also see security flaws often come from.
Integrating Security Into the Development Lifecycle
Security should be a factor in requirements gathering, design, implementation, testing, release and maintenance. In the design phase developers may identify what data is sensitive, trust boundaries, privileged actions and which are the possible attack vectors. In implementation we see that they should use secure coding practices and also go with proven APIs instead of rolling out custom security features. Code reviews at this stage will look at how the application handles untrusted data, credentials, access rights, file operations, and error handling. Also at the continuous integration stage we see automated checks which will catch certain issues before the code goes into production. At release time it is put that applications be tested in real world user permission sets and at scale as opposed to just a developer’s unrestricted environment. After going live teams should be on top of security advisories, get out patches for known issues and look into reports of out of the ordinary behavior or new found vulnerabilities.
A good testing approach includes a mix of positive and negative tests. In positive tests we see which authorized users are able to carry out what they are meant to do and in negative we see how the system handles out of band data, insufficient privileges, that which has expired session tokens and also unexpected file contents. Developers should see that errors do not expose secrets or leave the app in a state which may be open to attack. Security issues should be put forward based on how serious the issue is, how likely it is to be taken advantage of, and what the affected resources are. Teams should report on issues which remain open and make sure that fixes truly address root causes and not just patching up error messages. While auto tools and internal testing are a great start, for large scale apps we also see value in independent penetration testing, specialist code review, and other broad security reviews which the average dev may not think to do.
8. Importance of Security in Windows Programming
Secure Windows programming is an issue which still we see play out as companies use desktop software, internal business tools, system utilities, and applications which tie local machines to cloud services. As that software handles more sensitive info, developers must study how OS permissions, identity systems, file handling, networking, and third party components play into app security. Security is a cross cutting issue which plays out in many languages and frameworks as many of the base principles are the same. A developer working with C#, C+, WinUI, Windows Presentation Foundation or the Windows API still have to validate input from untrusted sources, protect credentials, enforce authorization, manage dependencies and test security assumptions. Also these skills play into web dev, cloud engineering, enterprise software and any other field which requires apps to protect data and operate reliably in untrusted environments.
The issue of secure software engineering’s growth is a result of the price of vulnerabilities and the fact that we must maintain software for the full term of its use. Employers and users benefit from developers who are able to identify risks at early stages, explain the tradeoffs between security and other factors, and put in place practical protections which do not make the applications hard to use. To build this skill set it is not enough to just know what the known issues are. Developers must study secure coding practices, be familiar with the relevant platform documentation, practice code review, get to know security testing tools, and follow in the reporting of vulnerabilities. Also they must recognize which areas of which they are limited in assessment and get in specialist help when the application’s complexity or risk requires it. Secure programming is a continuous process which includes technical know how, careful thought, working together, and a life long learning approach.
Conclusion
Windows application security is about to go in and fix that which causes exposure before the users, organizations, or computer systems are put at an unnecessary risk. We see improper input validation which in turn presents malicious data to affect app behavior, insecure storage of credentials which in turn exposes sensitive accounts, and large permission sets which in turn blow the results of a compromise out of proportion. Also we have unsafe file operations which may allow for unauthorized access or modification, and vulnerable dependencies which in turn can break otherwise secure code. Also weak auth and auth which puts sensitive resources at risk thus it is very important to verify identity and enforce permissions at the right places.
Devs can reduce these risks via parameterized queries, protected credential storage, use of least privilege access, safe file handling techniques, use of maintained dependencies, proven auth systems and also in regular security testing. Note that these do not remove all possible vulnerabilities and should not be looked at as a replacement for a full security audit or risk assessment. They do however form a practical base for building more resistant software. As Windows apps continue to play key roles in personal and professional settings secure software engineering will still be very much a value add for developers who are into creating reliable, maintainable and trusted apps.