Introduction
Financial cybersecurity is the technologies, policies and procedures that banks, brokerage houses, payment companies, and investment companies use to safeguard money, bank accounts and private financial data from the digital world. With more people managing their savings, transferring money, buying stocks and keeping track of investments on the web, it is essential to protect financial systems. To break into financial accounts, cybercriminals resort to phishing emails, stolen passwords, fake sites, malicious software and ID theft. These risks are mitigated through a combination of financial institutions’ security measures, including encryption, identity verification, transaction monitoring, access controls, and ongoing security testing. One defence is the use of multifactor authentication (MFA), which means users have to provide more than one form of identification to sign in. Learning about these security measures enables customers to become aware of the ways in which financial institutions safeguard their funds, and what they can do to limit their risk of falling victim to cybercrime.
Encryption: Shielding Information of Financial Nature that is Sensitive.
One of the main technologies that are utilized to protect financial data is encryption. This works by encoding data that is readable by converting it into a code that requires a decryption key to be rendered readable. Encryption helps banks safeguard both data in transit and sensitive data in databases and servers when it’s being sent from customers’ devices to their online banking services. Encryption, for instance, is used to keep unauthorized parties from reading the information passed from user to bank or from user to user during a banking login or money transfer over a secure connection. Data in transit over networks is often secured with Transport Layer Security (TLS) and data that is stored is often secured with strong encryption techniques. But no cyber-attack can be avoided when encryption is in place. Criminals could still gain access to financial services even if they get a customer’s login details or if they obtain a device that a customer has authorized to use. Hence, institutions combine a variety of other protective measures, such as encryption and authentication, with monitoring.
Using Multi Factor Authentication and Identity Verification
Usually, financial accounts have passwords as the initial line of defense, though not always. Phishing, weak passwords and a variety of websites using the same password are all ways for criminals to obtain a password. The loophole is overcome by multifactor authentication, which requires two or more types of evidence to prove someone’s identity. This is usually a password or some other form of identification that the user possesses, or a security key, or a fingerprint or facial characteristic. For example, a password may be entered into the investment site and, before access is granted, may also need to be approved via an authenticator application. In some institutions, passkeys or biometric verification is also employed as a way of improving account security. These techniques will make it harder for people to access computers and systems without permission, but no authentication technique can remove all risk. Customers should not give out their verification codes to anyone that calls or sends them a message that is supposed to be sent from their banks.
Secure Payment Processing and Tokenization.
The payment information is protected with tokens, which are substituted for the sensitive information, through tokenization. A payment system can instead of repeatedly exposing a customer’s actual card number during the supported transactions, expose a token representing the underlying information. The token is only valid for use in the respective system or context and the original payment details are kept and handled in line with the security arrangements of the provider. This technology is utilized in digital wallets, payments with cards, and beyond. When a customer pays with a supported mobile wallet, for instance, the merchant might not get the customer’s card number instead of a payment token. If the transaction information is later exposed, having the data tokenized will make it less useful. But, tokens need to be secured from misuse, and tokenization alone does not ensure that purchases are not fraudulent. It is thus used together with transaction verifying, encryption, monitoring and payment authorizing controls by financial institutions.
Real-Time Fraud Detection and Monitoring
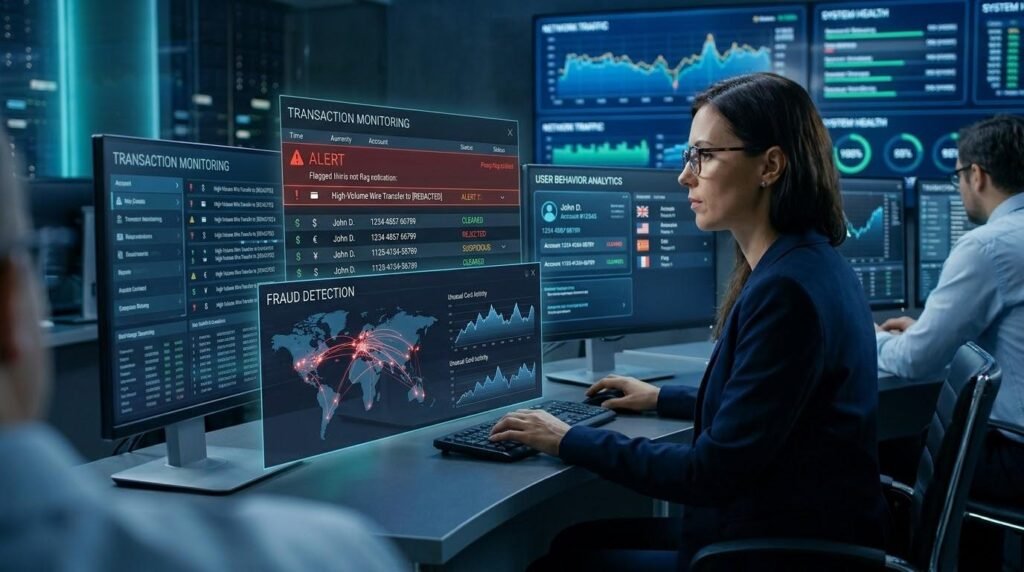
Money is dealt with in vast amounts every day by financial institutions and it would be impossible to check each and every transaction manually. Fraud monitoring systems can look at a transaction, activity, device information and behavioral patterns to determine if there are suspicious events. These systems can rely on pre-defined rules, statistical analysis and machine learning models to determine if an activity is similar to known fraud. If a customer who normally sends out small domestic payments, for instance, suddenly begins a number of unusually high payments from a new device, the bank’s monitoring system could trigger further verification of the customer. The institution may choose to delay the payment, ask for confirmation, deny the payment or send it to a fraud investigation team depending on the situation. Monitoring can also detect any repeated logon attempts, any unusual logon trends, and any possible account takeover attempts. However, sometimes normal customer activities can lead to false alarms and more sophisticated criminals can simulate normal customer transactions. Investigative techniques involving human resources and continually evolving detection methods are still critical components of a solid fraud prevention plan.
Security and Protection from Threats
Financial institutions need to not only monitor access by outside parties, but access by employees and contractors to sensitive systems as well as access by service providers. Access control policies help to control who accesses information, approves payments, can change records, or administer technology infrastructure. One of the most popular is role-based access control, where permissions are granted based on the role the individual has in their job. In the case of a customer service representative, for instance, he or she might be authorized to modify some of the information on the customer’s records, but not to approve big transfers or alter security settings without further permission. Access to accounts is given the lowest level of access needed to perform the tasks. Additionally, financial organizations could get rid of crucial responsibilities in order to make sure that one employee isn’t capable of starting and authorizing a high-risk transaction alone. Supervised accounts are protected with more security via enhanced authentication, activity monitoring and limited access. Routine reviews will also identify and eliminate unneeded permissions (including those that could be accidentally given to staff when they change jobs or leave institutions), which will help prevent unintended access and insider abuse.
Ensure API and Cloud Security.
Application programming interfaces (APIs) are increasingly used by banks and investment platforms as the way to integrate identity verification providers, mobile applications, payment processors, market data services and other financial technologies. Such links allow digital services to share information efficiently, which can be a problem if they aren’t properly secured, as it can lead to the exposure of customer information or unauthorized transactions. To safeguard APIs, financial institutions implement authentication and authorization processes, ensure secure communication with encryption, limit API rates, validate incoming data, and monitor usage. They can also employ security gateways to detect atypical requests, and limit access to critical functions. Cloud security is also critical because there are numerous financial institutions that host their applications, store their records and process their data in the cloud. Protecting cloud data requires careful data permission setup, data encryption, network segmentation, secure backups, vulnerability management and regular logging. Institutions need to be aware of the security roles that are held by the cloud provider, and those that are retained by the institution. While a provider’s reputation is one way to ensure a secure cloud environment, the environment must also be properly configured and monitored.
Avoiding Phishing and Identity Theft Attacks
The persistent threat of phishing attacks is that they don’t just exploit technical vulnerabilities, but human behavior as well. Impersonators might be able to look like they’re from a bank, investment firm or payment processor in emails, text messages or social media messages. Such messages can instigate a sense of urgency, such as an account being suspended or there being a suspicious transaction that needs to be confirmed. The victim could be redirected to a fake login site that is set up to obtain logon passwords, card information and verification codes. Another type of identity theft is when criminals obtain personal information from multiple sources and use it to assume the identity of a customer. Using stolen credentials, attackers can try to make account takeover; change recovery info; transfer money; and/or sell access to other criminals. Financial institutions protect themselves from these threats by detecting suspicious logins, recognizing devices, notifying customers, verifying their identities, and implementing account recovery measures. It is the customer’s responsibility to check any requests that come out of the blue, to not click on any suspicious links and to contact the institution through the official application or through the contact information published in the institution.
Incident Response and Financial Data Breach Management
With regard to financial cybersecurity, any incident may occur in any organization, regardless of how well it is protected, and a response and recovery strategy must be part of the cyber security plan. Incident response refers to the methodology of detecting, containing, investigating and recovering from security incidents. If a bank’s security team identifies an impacted account or potential data breach, they can suspend impacted accounts, isolate compromised systems, block suspicious transactions, and review system logs to identify the extent of the breach. Investigators then seek to determine the point of entry, to eliminate access to malware and to ensure that this ability is not taken advantage of in the future. There are several options to recover, such as restoration of clean backups, credential reset, testing of impacted services, and checking the integrity of financial data. Depending on the law and incident, the institution may have to notify the regulators, affected customers or other relevant parties. Although it is not a substitute for actual attacks, the regular practice of incident response exercises can help keep teams ready for real-life attacks and less confused during emergency situations. It is especially vital that the communication be clear when the customer has to be able to secure his account or challenge incorrect charges.
Actionable Advice on How to Save Money
While financial institutions are investing significant resources in cybersecurity, customers are also an integral part of the solution to account for their accounts. There are a few regular behaviors that can greatly minimize exposure to common threats.
- Use strong and unique passwords: Have a different password for each financial service and make use of a trusted password manager.
- Install multifactor authentication: Turn on other forms of authentication, if available, particularly phishing-resistant ones like security keys or passkeys.
- Confirm communications: Do not click on links that you didn’t expect from a bank, and avoid giving out passwords, PINs, and verification codes. If you are not sure, get in touch with the institution officially.
- Protect your devices: Do fill OS and App updates, use screen locks, and don’t use untrusted software.
- Check transactions: Periodically review account statements, investment activity and payment notices. Let your bank know of any transactions you don’t recognize right away.
- Use secure connections: Do not do sensitive financial transactions on untrusted public Wi-Fi Internet connections. Use a trusted network or mobile data connection, if possible.
- Secure account recovery details: Ensure that the account recovery details, such as registered email and phone number are kept secure as criminals may use these to reset financial account details.
- Quickly respond to suspicious activity: Contact your bank/broker; ask for appropriate account limitations; change compromised account numbers/credentials from a trusted device; follow the bank’s instructions.
These practices are in addition to institutional safeguards. It is important for customers to keep in mind that respective financial institutions shouldn’t require the customers’ password or one time security number to investigate a reported issue.
Conclusion
Financial cybersecurity involves a layered approach that ensures protection of money, personal data, payment mechanisms and investment services. Encryption helps to secure sensitive data, multifactor authentication further strengthens identity verification, tokenization minimizes exposure of payment information, and fraud monitoring helps to identify fraudulent transactions. Access controls restrict access to unnecessary permissions, and secure APIs and cloud configurations safeguard interwoven digital infrastructure. Incident response procedures are used to deal with failures in financial security and restore financial services in the event of attacks. But technology is not a solution to all threats, particularly those based on trust, stolen identities or human error. Therefore, there is a need to share the responsibility of maintaining a secure financial environment between banks, investment platforms, regulators and customers. Familiarizing themselves with these safeguards and implementing sound security practices can help people make informed decisions, identify suspicious behavior sooner, and minimize the risk of financial losses due to cybercrime.
Get more well researched information about Financial Cybersecurity here.