Introduction
Database security is very important in any organisation, to protect information crucial to business operations, decision making, managing relationships with customers and managing financial data. Within a database, sensitive information such as customer names and contact details, payments, staff information and confidential business information may be held. As organisations become more reliant on digital solutions, database security is becoming an increasing risk. Common threats include SQL injection attacks, ransomware, insider threats, data breaches and accidental exposure of information.
If just one vulnerability exists in a database, this can put thousands of records at risk, and cause disruption to a business, and damage to its reputation. Therefore, database security should be a key consideration for database administrators, developers and security teams. By following best practices in database security, businesses can effectively protect their data, ensure its integrity, and reduce the chances of expensive security incidences. Implementing secure database security will mean that only authorised users can read, change and manage sensitive information in a database.
Importance of Database Security
Database security includes a variety of processes, tools and methods, to protect database data from unauthorised changes or access, and from being lost or stolen. Database security in an organisation means that data can be kept private, accurate and accessible by authorised users at any point in time. If databases do not have secure protection, attackers may be able to access sensitive information if passwords are weak, outdated database software is used, insecure applications exist, or permissions are not set securely.
If customer payment information is in a poorly protected database in a business, a data breach may occur. This can lead to financial loss, legal actions, penalties from regulators and a loss in customer confidence. Database security can also help organisations prevent any inside threats. For example, staff members may accidentally leak confidential information, or access records they shouldn’t be accessing. To provide effective security, multiple security measures should be applied. To ensure secure data in a database, authentication, access controls, encryption, monitoring, regular maintenance and security policies should all be included.
Best Practice Database Security Measures
1. Secure Authentication
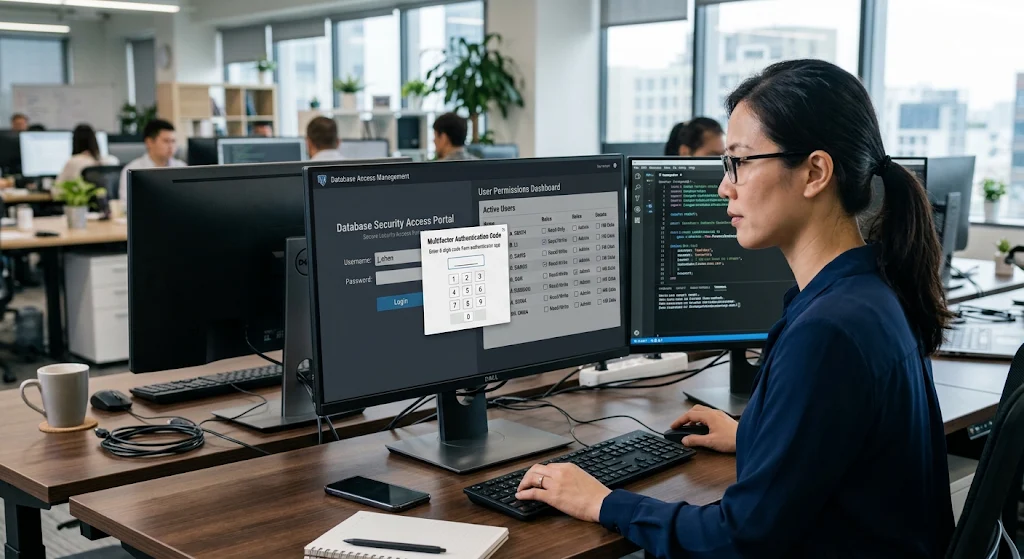
Within databases, strong authentication should be applied to ensure only authorised users and applications can access data. All accounts within a database should have strong and unique passwords. In addition, Multi-Factor Authentication (MFA) should be applied to increase security. Users should be required to prove their identity through 2 or more methods. This can include an authentication application, a security token, or another approved method. Therefore, even if a user’s password has been compromised, an attacker would struggle to access a database without the second form of verification.
For example, a finance company may require database administrators to type in a password and complete a second verification step before gaining access to sensitive customer information. Shared accounts should also be avoided within a database. This makes it impossible to know which user has performed which action. Within a database, each staff member and application should have a unique account with appropriate security requirements. In addition, database usernames and passwords should never be placed directly into an application’s source code, or within configuration files. By maintaining secure credentials in databases, unauthorised access can be minimised.
2. Role Based Access Control
Implementing role Based Access Control in your database will mean users only have access to information relevant to their role within a business. This means database administrators can give users specific permissions to view, alter, delete or manage information. Within a business, employees should be given a role which gives them certain permissions. For example, in a customer support team, users may be given permission to view customer contact details, but should not be given full access to financial information or database configuration. Accountants may require access to financial information, but should not have permission to change the employee information within the database.
Database administrators can give roles to different users within a database. This can include managers, developers, analysts and application users. Giving users roles in this way means that users only have access to information required for their role. Role Based Access Control means that data is less likely to be accidentally exposed, insider threats are minimised and permissions within a business are easy to manage. As a business grows, adding and removing employees becomes quicker and easier as users can simply be added or removed from a role.
3. Data Encryption
Encrypting data within a database will ensure sensitive information is protected. This is very important for holding customer information, financial data, staff information, passwords and confidential business data. Data should be encrypted both at rest and in transit. Data at rest refers to data stored in the database, within storage devices and within back ups. Data in transit refers to data being sent between applications, database servers and authorised users. Secure communication can be achieved using Transport Layer Security (TLS), whilst encryption can be implemented within databases. For example, within an online banking application, encryption can be used to protect financial information within a database and when customers access their accounts.
However, encryption keys within databases must be managed carefully. If the encryption keys within a database are not secure, then the whole encryption may be compromised. Restrict access to encryption keys, and implement secure processes for storing, rotating and recovering keys. Although encryption cannot guarantee there will be no security issues, it greatly reduces the chance that data will be exposed if unauthorized users can gain access to storage or network data.
4. Monitor Database Activity
Monitoring database activity means that unusual activity, suspicious access, or potentially harmful changes can be detected quickly. Database administrators can monitor connections, logins, queries and transactions made within the database. They can also monitor changes to permissions. By monitoring database activity, administrators can understand what is happening within the database, and if actions follow security policy. If unusual activity is detected, such as a staff member with typically low access to customer records making a large number of record requests in a short timeframe, an alert may be raised.
Administrators can investigate to find out if the activity was a legitimate business activity, an account being compromised or potential insider threats. Tools can be used to detect unusual activity, such as multiple failed login attempts, unexpected admin access, unusual connections, and suspicious changes to key records. Appropriate alerts should be set to notify of urgent issues. Security teams should regularly look at monitoring data within databases. Monitoring database activity can help identify potential threats in a timely manner, and mean that issues can be resolved quickly. This means that database administrators can have greater control over sensitive data in the business.
5. Apply Regular Security Updates/Patches
It is important that database management systems are kept up to date to prevent vulnerabilities in the system. Security patches and updates are regularly released by vendors to resolve vulnerabilities, increase stability and respond to new threats. If updates are not regularly applied to databases, the database may be vulnerable to known vulnerabilities. Database administrators should apply regular patches to update databases. They should look at what updates are available, consider how important the updates are, test them, and apply them appropriately. For example, in a database running either Microsoft SQL, MySQL, PostgreSQL or Oracle Database, administrators should regularly check for security updates for the database from the official vendor.
These updates should be applied to the database on a regular schedule. Before applying patches in a production environment, testing should be completed in development/staging environments to ensure any compatibility issues that may affect business operations can be identified. Reliable back up and recovery processes should be in place before performing major updates. Unsupported versions should be avoided as they may no longer receive key security updates. By regularly applying patches, databases are less likely to be vulnerable to known threats. This means a secure and reliable database can be created.
6. Regular Vulnerability Scans
Carrying out regular vulnerability scans can help identify vulnerabilities within databases, so that they can be resolved before they can be exploited by attackers. Vulnerability scans look at how secure the database configuration, versions of software, user permissions, network configuration, authentication and other security controls are. Database administrators can carry out vulnerability scans manually, or by using automated tools or security scanners. As an example, a vulnerability scan may show that default admin accounts have not been changed, there are unnecessary network connections, or the database is running on outdated software with known vulnerabilities.
It may also identify that users have too many permissions, or that services within the database can be accessed from unauthorised networks. If vulnerabilities are found within a database, their severity should be assessed. Those with the highest severity should be prioritised to be fixed. Vulnerabilities that put sensitive customer or financial data at risk should be fixed immediately. Vulnerability scans should be carried out regularly, or when significant changes have been made to databases. Performing regular security testing in databases will also help to determine whether improvements made in the past are still effective. By proactively identifying and fixing vulnerabilities, database administrators can reduce the attack surface of the database, and improve resistance to cyber attacks.
7. Secure Network Access
As databases often interact with applications, devices used by staff members, cloud systems and other systems within an organisation, it is important to secure network access. If network services are not correctly secured, attackers could access the database server and sensitive data. Database administrators should work with network security teams to ensure only authorised systems and users can connect to databases. Firewalls can be used to limit network traffic. Only necessary network connections can be allowed, and unauthorized connections can be blocked. Where possible, network segmentation should also be implemented.
This means separating database servers from the public facing systems, or other parts of the network. For example, in an e-commerce business, customer data can be stored on an internal secure network. The database can only be accessed via approved application servers within the business. This can reduce the chance of attackers connecting directly to the database if another system within the business’ network has been compromised. If remote database access is required, secure connections, correct authentication and limited access should be applied. Any un-necessary ports in the database should be disabled. Database management should not be directly accessible from the public internet. Applying secure network security measures can reduce unauthorised network connections, and provide additional protection to important data within an organisation.
8. Secure Configuration
Databases should be configured in line with security best practice. Unnecessary components should be removed to reduce opportunities for attackers. Database software may contain default accounts, sample databases, examples and services which may not be required for normal operation of the business. If these components are left in place within the database, unnecessary vulnerabilities may be introduced. Default admin credentials should be changed, and un-necessary accounts removed. Un-used databases should be removed. Services should be limited to the minimum required. In addition, database servers should run using OS accounts with limited permissions.
For example, when implementing a new PostgreSQL database in a company, administrators should ensure the authentication method is secure. Un-necessary network connections should be limited, secure connections should be made, and un-needed services removed. Within configuration, configuration files should be secure. Database credentials should be stored securely. Development and test databases should be separated from production databases. Security best practice and guidelines from vendors can be followed to ensure secure configuration. Regular checks should be performed on configuration. Changes to systems, updates in software, and new applications may create configuration within systems that may reduce current security.
9. Robust Logging
Logging within databases can help determine who has done what, and hold users accountable. Logs can indicate successful/failed logins, changes in user permissions, changes in sensitive data, admin changes and key changes in database configuration. If an issue occurs in security within a database, logs can help database administrators identify which account/user may have caused the issue. For example, if unauthorised changes were made to employee records, logging within the database can help determine which account made the change, and when. Logging can also help businesses comply with data protection requirements, and internal security policies.
However, logging should also be protected from modification/deletion by unauthorised users. Database logs should be limited to only those with authorisation, and should be kept for an appropriate period of time. Key events should be regularly reviewed. In addition, sensitive data such as passwords or confidential values should not be logged unnecessarily. Combining logging with monitoring within a database can provide more insight into activity within databases. It can make it easier to investigate suspicious activity, hold users accountable, and improve security within an organisation.
10. Managing User Permissions
Users within a database should only be granted the level of permissions required to complete a task. Applying the principle of least privilege ensures that users do not have access to excess information. Even if users are authenticated, they should not be given full access to all databases, tables and admin functions. For example, if a reporting application is linked to a database, it may only require read access to sales data. It may not require the ability to delete customer data, alter database configurations, or create admin accounts. Database administrators should avoid using powerful accounts (such as root, sa or other default admin accounts) to perform normal operations for applications. Instead, specific accounts should be created for admins, applications, developers and reporting services with clear permissions.
If employees change roles, leave the business, or no longer require specific access to data, their permissions should be reviewed. If a temporary admin permission is required for a task, it should be removed once the approved task is complete. Regularly reviewing user permissions can help identify any unnecessary access. It also means that if an account is compromised, the impact will be reduced. It also means staff members will be unable to access information outside of their role. It is particularly important in organisations where many departments share a common database infrastructure.
11. Protection against SQL Injection Attacks
SQL injection occurs when user inputs are not correctly handled in an application, meaning that attackers may be able to interfere with database operations, access unauthorised data, or unauthorised changes to data. This often occurs when user input is directly inserted into SQL queries, without secure handling. For example, an online sign up application may be vulnerable to SQL injection if user input in forms is directly inserted into database queries, and user input is not separated from database commands. To prevent these vulnerabilities, database administrators and developers should work together.
Parameterised queries, prepared statements, correct input validation and secure development methods should be applied. Parameterised queries mean that user input is treated as pure data. Application accounts should also not be given excess admin permissions, as this can increase the damage caused if an SQL injection occurs. Regular testing of application security, and code reviews can identify any unsafe interactions with databases. As database security relies on secure database configurations, and secure application design. It is important that database administrators, developers and security staff work together to protect databases from SQL injection.
12. Secure Backup and Recovery Processes
Backups in databases are very important in protecting data in case of ransomware, accidental deletion, hardware issues, software issues or other issues causing data loss. However, if a security issue occurs, attackers may be able to access, change, encrypt or delete backup data. Reliable back up schedules should be in place to back up data, depending on how important the data is, and what recovery requirements the organisation has. Back up data should be encrypted, have restrictive permissions, and be stored in a different location to the main database. Where possible, offline or immutable backups should be kept to reduce the possibility of unauthorised users altering or deleting data.
For example, in hospitals, regular backups of patient data can be taken. This means that in the case of a system failure, or Ransomware, essential information can be recovered. Regular checks should be made to ensure backups can be restored, and that data within backups is complete, accessible and usable. Roles in recovery should be documented, and clear recovery processes should be in place. Having efficient backup and recovery processes means less downtime in the business, business operations can be maintained, and organisations have reliable processes in place for recovering important data in unexpected situations.
Common Database Security Risks
- SQL Injection and Unauthorised Access
SQL injection is a serious risk in database security. If applications interacting with databases do not implement secure queries, attackers may be able to interfere with queries. This may mean unauthorised data can be accessed. Unauthorised access can occur due to compromised credentials, weak user authentication, excessive permissions or poorly secured admin accounts. This poses a problem in organisations storing customer data, financial data and confidential business data. To protect against this risk, database administrators should work with developers to ensure application security is good.
Strong user authentication should be implemented, and users should be given limited permissions. Any unusual activity should be monitored. Organisations should also have processes in place to deal with compromised credentials, and investigate suspicious access. As attackers may exploit vulnerabilities in applications, user accounts, network connections, or database configuration, multiple security measures should be placed in place to protect databases. Multiple security measures will make it harder for unauthorised users to access sensitive data, even if one form of security fails.
- Ransomware and Misconfiguration
Ransomware can be a threat to organisations as it can prevent access to business data. It may lock data or systems so that it can no longer be accessed until a ransom is paid. If ransomware affects a database, this can cause operational disruption. If secure back ups are not in place, it may be very expensive to recover from the issue. If database configurations are incorrect, serious risks may occur. If permissions for database access, database services, default credentials and excessive permissions are not correctly configured, unauthorized access may occur. For example, if a database in the cloud has been accidentally made publicly accessible, sensitive data may be exposed to people outside of the organisation.
Database configurations should be regularly checked, and network connections should be limited. Admin accounts should be secure, and secure back ups should be in place. Organisations should also have processes in place to respond to incidents. This should detail how suspicious activity should be detected, systems affected by threats should be contained, and services should be safely restored. Understanding these risks can help database administrators identify any vulnerabilities and improve security within the organisation.
- Internal Threats
It is common for database security issues to occur due to issues caused by internal users. Users such as staff members, contractors, or developers may cause security issues intentionally, carelessly or accidentally. A staff member may gain access to sensitive data, or pass sensitive data to the wrong people. Alternatively, they may accidentally expose sensitive login details. A developer may accidentally make a configuration file public which contains login details for the database. They may also accidently move sensitive customer data to an insecure testing environment. Internal threats are therefore an issue to be addressed in securing databases.
Implementing role based access, controlling user privileges, and monitoring and auditing databases can help to reduce the risk of users causing security issues. Additionally, providing staff with security awareness training will enable them to know how to correctly handle sensitive data. Policies should be put in place to specify how sensitive data should be accessed, stored, moved and shared. By combining security measures, and educating employees on good practice, accidental exposure can be reduced. Therefore potential damaging actions within databases can be more easily identified.
Creating an Effective Database Security Policy
A good database security policy should clearly outline how information within an organisation is protected. It should include who has access to databases, what privileges users have, authentication methods, and security considerations. It should also include consideration for data encryption, management of backups, testing for vulnerabilities, updating software, monitoring databases, and assigning responsibility for responding to security issues. In an organisation, users may be required to have unique accounts, and sharing database logins may not be allowed. Additionally, accessing highly sensitive financial/customer data may require approval from managers. The policy should include processes for reviewing user privileges, deleting inactive accounts, raising concerns about suspicious activity, and responding to security issues.
In addition, the policy should include how long audit logs and backups need to be kept, depending on legal/operational requirements. Database administrators, developers, management and security professionals should be involved in establishing/reviewing the policies to ensure they address risks within the organisation. As the company changes, technology is updated and new security threats appear, policies should be regularly updated. This, alongside training employees, ensures that requirements for securing databases are up to date and consistently applied.
Conclusion
Securing databases is extremely important for organisations as they rely on digital data in order to conduct operations, provide services to customers and make key business decisions. Given that databases are often vulnerable to cyber threats, administrators should implement various measures to prevent unauthorized access, ransomware attacks, SQL injection, internal threats and accidental exposure of sensitive data. Implementing the 12 best practices outlined in this article can create much more secure databases. These include: ensuring strong authentication, role based access, encrypting sensitive data, monitoring databases, applying security updates, identifying vulnerabilities, improving network security, secure configurations, database auditing, managing user privileges, preventing SQL injection, and securing backups.
However, to ensure effective database security, it is vital that security measures are regularly reviewed, policies updated, employees provided with training, and measures taken to address new threats. If database administrators take these measures, they can limit security risks in databases, maintain data integrity, ensure customer confidence, and allow business continuity. Overall, an effective approach to database security allows organisations to sensibly manage information. This can create a more reliable digital infrastructure within companies.