Introduction to Machine Learning in Cybersecurity
Cybersecurity is a key element as we see individuals, businesses, government agencies, and financial institutions to be ever more dependent on connected systems which they use to store info, pass info, and conduct transactions which in turn has put forth more of a target for cyber criminals to go after. We see traditional security measures like firewalls, anti virus programs, and pre determined security rules as very much still relevant but they do have their issue of not detecting unknown threats which do not fit into what was previously identified as an attack. In to this comes machine learning which provides a different solution by way of systems which are able to analyze large data sets, recognize trends, and which in turn are able to identify what may be a security issue. As opposed to a sole reliance on man made rules, machine learning models are able to study from history and use that info to put together a response to the new events. This in turn gives security teams better response to what is suspicious and to look into what may be an attack before it does large damage.
Machine learning is a division of artificial intelligence which has computers systems train on data they are given to recognize trends. In the field of cyber security these models look at network traffic, login attempts, email traffic, software action, and financial transactions to tell the difference between the normal and the potentially harmful. For example a system may note that a staff member usually accesses company resources during the day from the same device. If that same user attempts to access sensitive info from a different device at 2am the system will flag this out. This does not mean the account has been taken over but it does give security teams a reason to look into it. By use of automatic analysis combined with human input machine learning improves digital security and helps organizations deal with the ever growing issue of complex tech based threats.
What is Machine Learning in Cybersecurity?
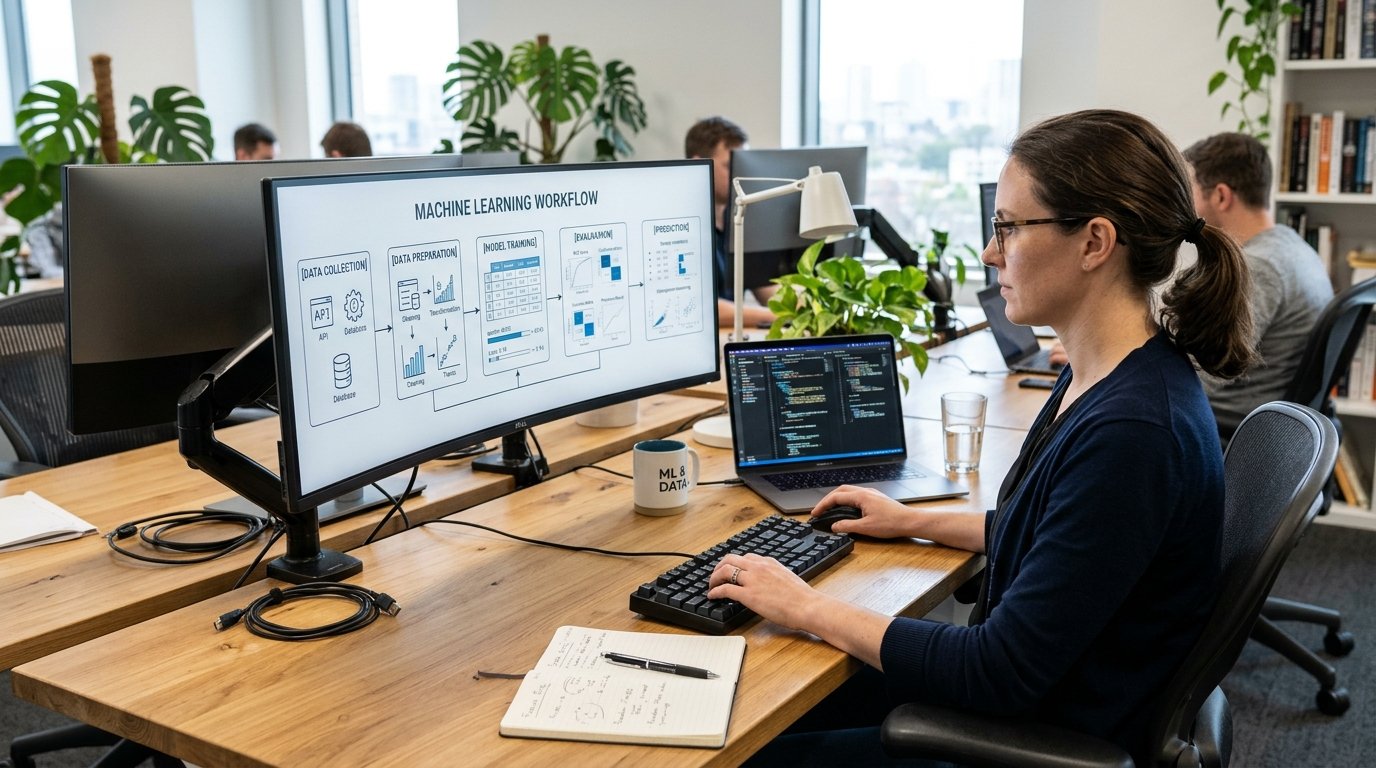
Machine learning in the field of cybersecurity is to start by gathering info from what is to network devices, servers, computers, authentication systems, email gateways, and security apps. What we collect may include connection times, IP addresses, login locations, file access logs, which processes of software are at play, and how devices communicate with each other. Also before a model is able to do this analysis well the data has to be cleaned up, organized and turned into what are useful features. Which are measurable variables that help the model to recognize patterns for example the number of failed logins in a given time frame or the amount of info a device puts out.
Also which security issue we are trying to address will determine if we train the model with what is known to be bad and good activity or we let it figure it out from the data without us putting in pre determined labels. The model in turn looks at new info and reports back with predictions, classifications or risk scores which in turn guide in what to look into more and what security decisions to make.
i. Identifying Normal Behavior Patterns.
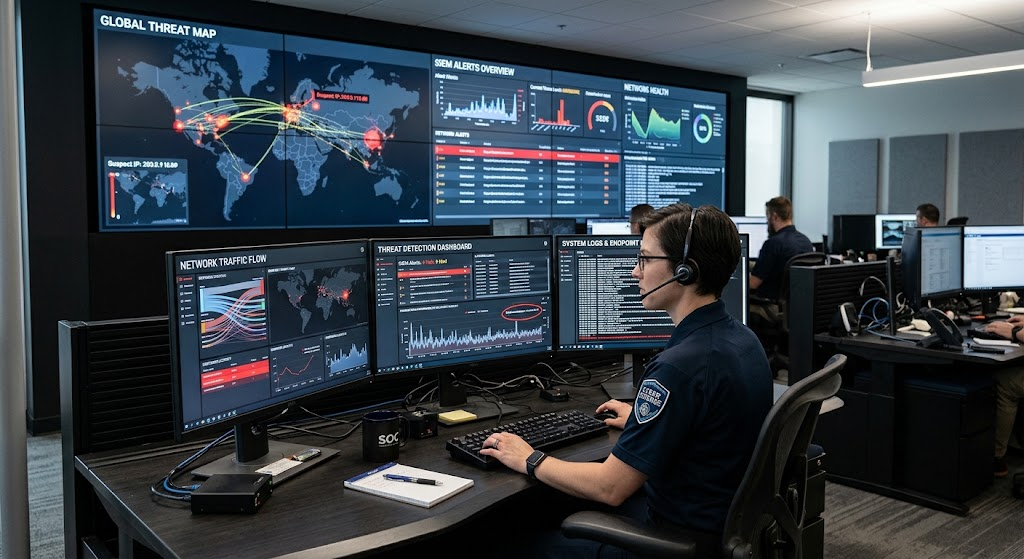
In the field of cybersecurity machine learning plays a key role in setting a baseline for what is considered normal behavior. A baseline is that which we see as the typical of what transpires in a given environment, account, network, or computer system. For instance a business network will tend to have routine traffic flows during work hours and an individual account may see the same set of applications accessed on a regular basis. What we see as routine the machine learning models look at in the past to determine what is the norm and to what is to be expected.
When new behavior is very different from what is base lined in as normal the system will flag it as an anomaly. Unusual events may include large spikes in data transfer, frequent failed log in attempts, a new machine connecting to a critical server, or an account that uses different sets of files then what is usual for that account. But also an anomaly is not the same as a breach for we see that which is out of the ordinary also to include valid changes like remote work or a new project. Thus what is identified as an anomaly is in fact the start of an investigation and not a confirmed case of misdeed.
ii. Detecting Threats Across Various Learning Models.
Different machine learning strategies which play to the strengths of different elements of cybersecurity. In supervised learning we train a model with labeled examples that include both sides of a binary issue for it to learn from, say what is a good email and what is junk or what is a safe piece of software and what is a virus. Unsupervised learning has the model looking at the data without that pre determined labeled set and so may see out of the ordinary issues that may have gone by unnoticed before. Also there is semi-supervised learning that is a mix of some labeled and large scale unlabeled data and other models which do well off of a little bit of normal activity data and flag what is out of the ordinary.
What you choose depends on what data you have, what the threat is, and the results of a bad prediction. For example supervised learning works well when we have a history of what we know to be attacks, and also we can use anomaly detection to bring to light what is out of the ordinary we may not have seen before. In the real world we see these models used together with basic security rules to better detect issues. Also models have to be put to the test and improved over time because as tech changes, user behavior changes and attackers change their methods which in turn makes what may have been very useful models not as so.
Major Uses of Machine Learning in Cybersecurity.
Identifying what causes the breach of digital systems’ confidence, integrity, or availability. We present here how machine learning may be used by organizations to detect out of the ordinary events, to put in order which security alerts are most important, and to better react to possible incidents.
i. Detection of Out of the Ordinary Network Behavior.
Computer networks produce large sets of data as devices interact with servers, applications, and external services. Manual monitoring of all connections is a challenge especially so for organizations that run large scale networks with thousands of devices. Machine learning systems can analyze the network traffic to notice out of the ordinary communication trends, atypical connection attempts and sudden changes of data flow. For instance a computer that starts to talk to unknown external servers or to move very large sets of info may draw extra notice.
Also we see models that note in account for repeated attempts at connection, scanning actions, and possibly data theft. What they find helps security teams look into if a device is infected or if an app is acting out of the ordinary. Also it is true that network anomalies may also have valid reasons like software updates, system backups, and high customer demand. Thus it is best for companies to use machine learning reports with network logs, threat intelligence, access controls, and other security tools before determining what if any action is required on a reported issue or if more research is needed.
ii. Identifying Atypical Account Activity.
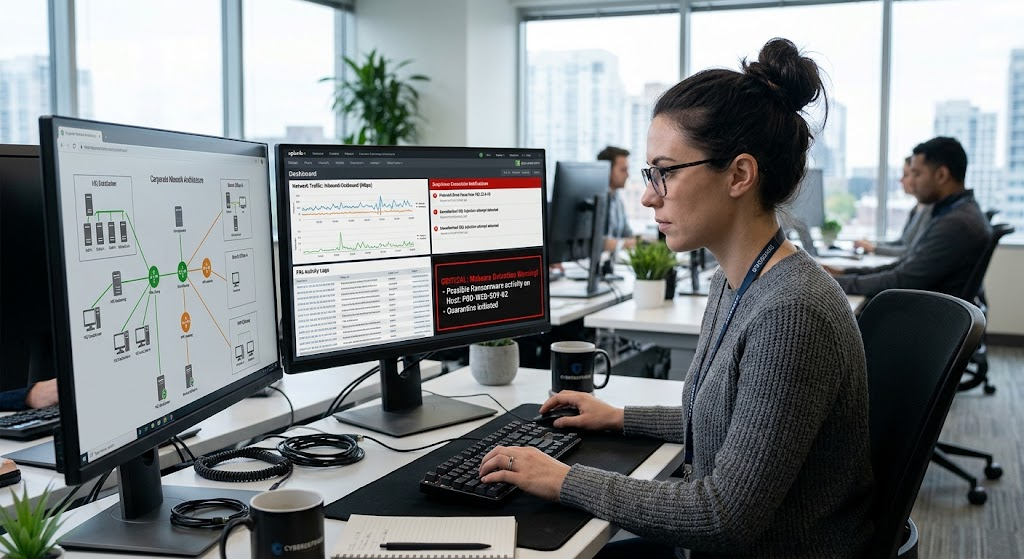
Account compromise is an issue which we see often in security because attackers use stolen passwords, phishing links, or leaked info to get into digital services without permission. We use machine learning to identify out of the ordinary account activity by which a login time, device info, access location, auth failure, and which resources an account tries to use are looked at. A model may see a log in from a new device which is then followed by quick access to private files, especially when that is out of the account’s norm.
Also it will note out of sequence actions like an account which tries to get into many systems in a short time. Also it may report atypical patterns of use. As per what the org’s security policy is, these may bring up extra auth questions, short term locks out, or a note for the security analyst. But also it is the case that real users do travel, change devices, or go out of their normal routine. So security systems have to look at many variables and the import of the requested resource before they label each odd login as an attack.
iii. Types of Malware and Malicious Software.
Malicious software which we refer to as malware includes programs that carry out actions like info theft, system disruption, user spying, and unauthorized access to devices. Present anti virus solutions use signatures of what is known bad which they look for in files, but attackers’ modification of malware into new variants which do not match those signatures is an issue. We see machine learning as a way to support signature based detection which looks at file structure, code, program action, and the OS interaction.
For instance a model may note a program which touches many files, which makes unexpected network connections, or which gets sensitive info for no reason. Also some systems look at files before they run, and some watch action as programs are running. While these methods do what they can to identify new malware they are not a sure thing. Also what is good software can present suspicious features and very sophisticated malware is made to look like it is harmless. Thus for effective malware protection we see a mix of machine learning with what we have in antivirus today, application security, sandbox study, and timely security updates.
iv. Fighting Off Spam and Phishing Attempts.
Email is a key medium for business and personal use but also a primary platform for distribution of spam, phishing attempts, malware in attachments, and fraud. We see machine learning play a large role in email analysis which includes study of email body text, sender info, message structure, included links and other features to determine if a message is a threat. A trained model which uses labeled email data may learn to识别 suspicious language, pass off sender info, out of character links, and emails that mimic trusted companies.
Also more complex systems use domain reputation, attachment scan results and info on a sender’s typical email behavior. Upon detection of a bad message the system may send it to the spam folder, put it in quarantine, or alert the recipient. But attackers are always evolving their tactics and some phishing emails are very well done to look like real business emails. Also filter systems aren’t perfect and may let through bad emails or flag good ones. It is important that employees are aware of this and to verify requests which include password info, confidence data, or financial transfer which come out of the blue.
v. Identifying Possible Cases of Fraud.
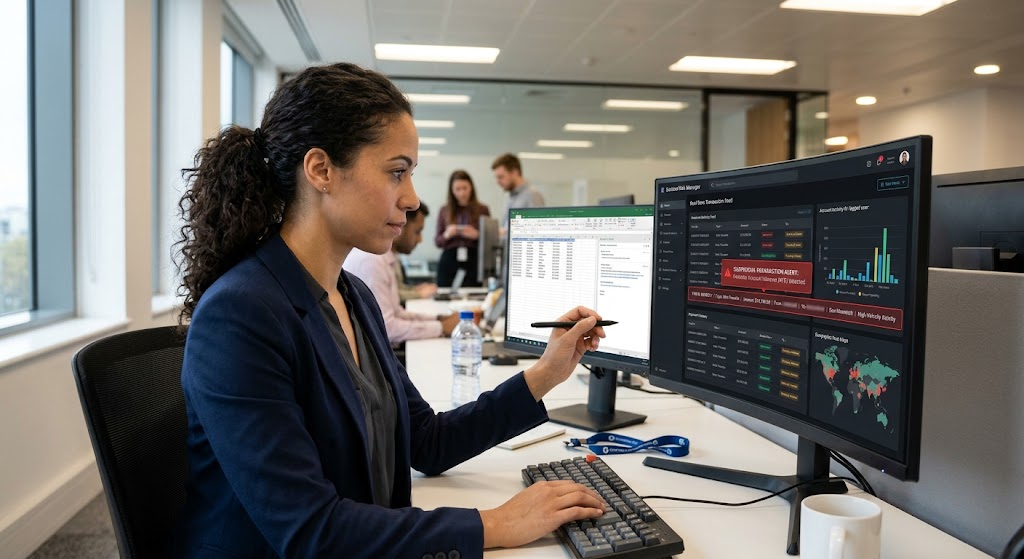
Financial institutions, online stores, payment companies, and digital banking services report daily on large volumes of transactions which in turn makes automated fraud detection very valuable. We see that machine learning models look at transaction amounts, payment frequency, merchant info, account history, device features and other related variables to put together a picture of what is a suspicious transaction. For instance an account which mostly does small domestic purchases may all of a sudden go after large value transactions from a different device. The system will compare this to what is usual for that account based on history and will give a risk score which in turn determines what action to take.
We see accounts that had been doing mainly small domestic purchases suddenly going after high value transactions from a new device. This is put into perspective with what we have seen out of that account’s past and we will assign a risk score to determine if we should ask for more info, put the trans up for a second look, put it on hold, or take it to a live person. Also what may seem out of the ordinary is not always fraudulent, so companies have to walk a fine line between effective fraud prevention and customer experience, also they have to be fair and not put forth what may be a good purchase by a customer at risk. This process supports flagging potentially fraudulent transactions, allowing organizations to identify payments that may require closer examination.
Machine Learning in Anomaly Detection.
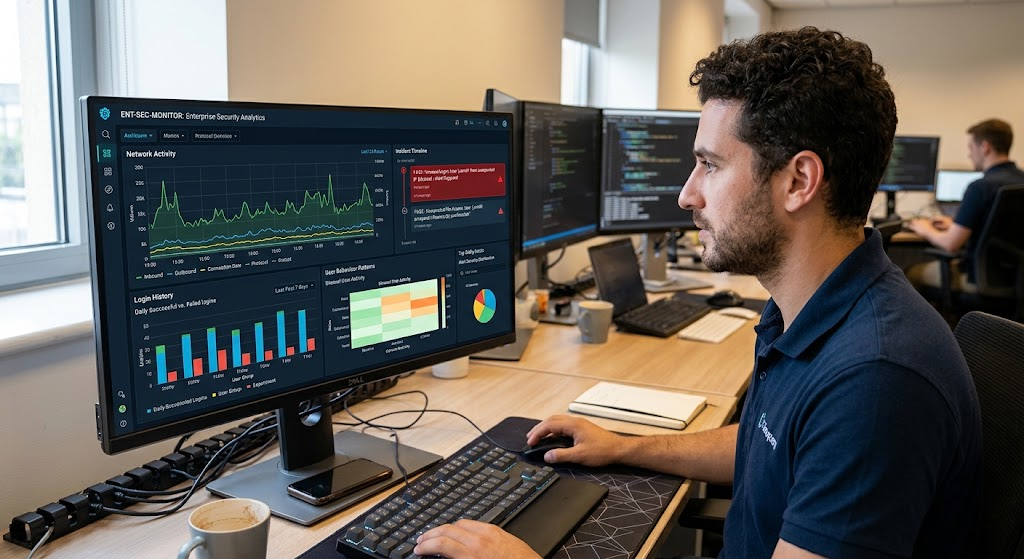
Anomaly detection is a large piece of the security in which machine learning plays many attacks present with action which is out of the ordinary for that which is usual in the system. To that end a model will look at past data, learn from what is typical in that data, and set what is normal as the baseline. For example a server may usually exchange a set volume of info with certain internal systems. Should that same server start to send large amounts of data out to new and unknown places that model will put out an alert. Also we see in large numbers of failed login attempts, changes in account permissions which are out of the ordinary, or devices which are active at off hours. The model looks at the degree, how often, and the combination of these issues to see what requires a look. Some systems will use basic stats for this, some will use more in depth methods which may group like actions together or which may learn relationships between many variables. The goal is to find what is important to look at without at the same time flooding security teams with reports of run of the mill changes.
Anomaly detection is improved when we take into account the context instead of looking at a single out of the ordinary event. For instance a login from a new location may be fine if the user is traveling, but the same login is more out of the ordinary if it is followed by a series of password changes, access to very private files, and large data downloads. Also a system which puts together these different signals may present a higher risk assessment than one which looks at the login location by itself. Also companies can use info regarding job functions, device ownership, business hours, and which resources are most sensitive to better gauge what is going on. That said, models do not always fully understand the point of an event and may be thrown off by missing info or changes in how things are done. In which case human analysis is still very much a key element in looking at the alerts, finding out more info, and what to do next. This mix of machine learning for pattern recognition and human input makes for a better and more reliable anomaly detection.
Benefits of Machine learning in Cybersecurity
Some models are retrained with the latest examples and best data which in turn improves their performance in identifying new threats. Also machine learning may do away with routine work by which we mean it will prioritize alerts and very much take care of certain low risk tasks as per well thought out policies.
But it’s at the discretion of the quality of the data we put in, the right choice of model and how well an organization reacts to what the models present that determine the results. Machine learning greatly enhances cyber security when it supports proven security practices instead of which it is the sole agent of security.
Problems with Machine Learning for Cybersecurity.
Despite what machine learning does well, it also has its breaks and is not to be counted on for 100% in the world of cyber attacks. What it does is based in large part on the info it is given, how the models are put together, the methods which are used to check how well it is doing, and the setting in which it is operating. Also in play is the ever changing nature of the cybersecurity field as we see the adoption of new tech by organizations and attackers which are constantly coming up with new tactics.
These issues mean that auto detection systems must be a work in progress always monitored, maintained, improved. Also key is that which organizations do not put all their eggs in the machine learning basket we must have a working knowledge of these limits because to do so we run the risk of ignoring real issues or over reacting to what is in fact normal activity.
i. False Positives and Negative Predictions.
A false positive is when a system reports that which is in fact legitimate as a threat, while a false negative is the failure of a system to report a real threat. Both of these are issues for cyber security teams. Too many false positives may flood analysts with unuseful alerts, delay into investigation, and put business operations out of whack when they go after the wrong accounts or transactions. False negatives are even more of an issue as the bad guys may go right on with what they are doing without being noticed. For instance a model may flag an employee’s foreign based login as suspicious while at the same time not noticing a very well disguised attempt at data theft.
Orgs can reduce the risk of these by looking at what they put in as thresholds for detection, use of many different signals, review of what those alerts are telling us and to also measure how we are doin’ against representative data. Also diff applications may require a trade off between sensitivity and convenience. A very large financial transfer may call for more identification, while an everyday login may go through without much disruption. Regular review helps security teams to find out what is weak in their systems and to change out what isn’t working based on the results of what went before.
ii. Growing Attack Methods.
Cyber criminals are constantly changing their tactics to evade detection, exploit what is new in vulnerabilities, and profit from tech changes. We see malware which may have changed from what was before, phishing which uses more convincing language, and attackers which will present as normal user action. Also a model which did a great job with past threats may do poorly with what is unfamiliar to it. This is at times put forward as concept drift which is when what we see in the data changes over time.
For example a company’s usual network activity may greatly change after they introduce cloud services or allow remote work. If the model is not made current to include these changes out go the false alerts and in goes relevant threats. What we are saying is companies should monitor model performance, look at what the latest threats are, update training data as needed, and test detection systems on new scenarios. Effective protection is a continuous process not a one time machine learning tool install.
iii. Unfair or Incomplete Training Data.
Machine learning models require high quality and representative training data. If that data is riddled with errors, missing information, out of date examples, or has a very unrepresentative set of threats the resulting model will in turn put out poor quality predictions. For example a fraud detection system which is mainly fed data from one customer segment may do a poor job at evaluating customers with different spending behaviors. Also an account security model may flag up as suspicious what is in fact normal behavior if it is trained on examples which do not include remote workers, travelers, or people using assistive technologies.
In cyber security we see that biased data sets lead to over restriction of accounts, poor fraud detection which may be too aggressive or too lenient, or in some cases completely missing threats in underrepresented areas. Orgs should look for data gaps, check model performance across relevant groups and operating conditions, and also don’t assume that high overall accuracy is the same as good performance in all areas. Also they should look at privacy issues and collect only what is needed for security purposes. Careful data governance is the key to putting out fair, reliable and practical machine learning products.
iv. Efforts at Evading Machine Learning Detection.
Attackers will put forward specific strategies to decrease the chance of being caught out by machine learning systems. This is a part of what we see in adversarial machine learning, a field in which a red team will use a model’s weak points or flaws in the detection process to their advantage. For instance, a bad actor may present a benign face to the machine’s prying eyes by putting out a virus that looks like regular traffic, also an attacker will break up their attack over a long time instead of a short to reduce the look of something out of the ordinary. Also fraudsters may play around with transactions to go under the radar of auto check.
What is clear from these actions is that which models a company has in place needs to be used as just part of a large scale defense approach. Also at the same time, companies should have many security measures in place from multi layered security to behavioral monitoring to threat intelligence and also to that of independent verification. At the same time security teams must test their systems out in real world situations and also look into how good they are at spotting out of the ordinary threats. It is also important to note that no model is a safe haven from these attacks, therefore machine learning must be looked at as a single piece of a total defense system.
Combining Machine Learning with Human Input and Protected Measures.
Machine learning works best in a partnership with cybersecurity personnel and in association with present security measures. While machines may analyze the data and report out of ordinary events, human analysis is what sets things straight. They are the ones who sort out the complex issues, which business impact is present, and what is the best course of action. For instance a report of large scale data transfer may be a cyber attack, a routine backup, or an authorized change in which data goes from one system to another. The security pro will go in and look at the background info which supports the event in question and determine the most likely scenario.
Also it is very important that we have in place base level protections like strong auth, least privilege access, good backup practices, network segmentation, encryption and firewalls which are tuned just right. Also we must take care of known vulnerabilities which tech can’t cover. Also staff training, incident response plans and set procedures also play a big role in security. When you put auto detection with all of this out in the open you will see better results in your threat assessment but do not think tech will do away with all your cyber issues.
The Future of Machine Learning in Cybersecurity
Machine learning is going to be a key element in cybersecurity as we see an increase in the interconnectivity of digital systems and a growth in the amount of security info out there. We’ll see progress in behavioral analysis, automatic investigation, and the use of many security data sources which in turn may help organizations do a better job of recognizing complex attack patterns. For instance in the future we may see systems that are better at tying together strange account activity with atypical network communication and what may be perils of files which in turn will enable security teams to look at related events from a single interface.
But improvements in automation also require very careful attention, especially as we allow systems to block accounts, isolate devices, or disrupt business processes without immediate human input. Organizations will have to look at model accuracy, protect sensitive info, watch for changes in threat behavior, and put in place clear responsibility for automated decisions. The long term value of machine learning will thus not only be in more advanced algorithms but also in responsible implementation, secure practices, and people that are able to interpret what the tech is telling us.
Conclusion
Machine learning has indeed become a tool of value in cybersecurity which is a result of its ability to analyze large data sets, recognize behavior patterns, and identify what may be a threat or fraud. We see its use in the monitoring of network traffic, detection of atypical account activity, classification of malware, filtering out suspicious email, and the identification of what may be a fraudulent transaction. Also it is through the use of past data and evaluation of present events against what is known that machine learning systems are able to help organizations to better put into perspective which investigations to do first and to react more so to what is suspicious. That said these systems do have very important limits which include false positive reports, failure to recognize some threats, attack methods which are always evolving, use of biased training data, and attackers’ methods to go under the radar.
Thus their results must be taken with a grain of salt and are best used when put to the test and maintained on an ongoing basis. In the end effective cyber security is a much greater picture. What we see is that companies must put together machine learning with great security personnel, in place of known safeguards, regular software updates, responsible data use, and good incident response which together will allow businesses and individuals to benefit from smart threat detection but also to be aware that the protection of digital systems is a constant task.